A2P SMS Queue Expiration and Purging: How to Prevent Late Deliveries
A practical guide to distinguishing your own queue’s expiration, the expiry requested from your provider, and the message’s functional validity—with controls for OTPs, alerts, and auditable purges.
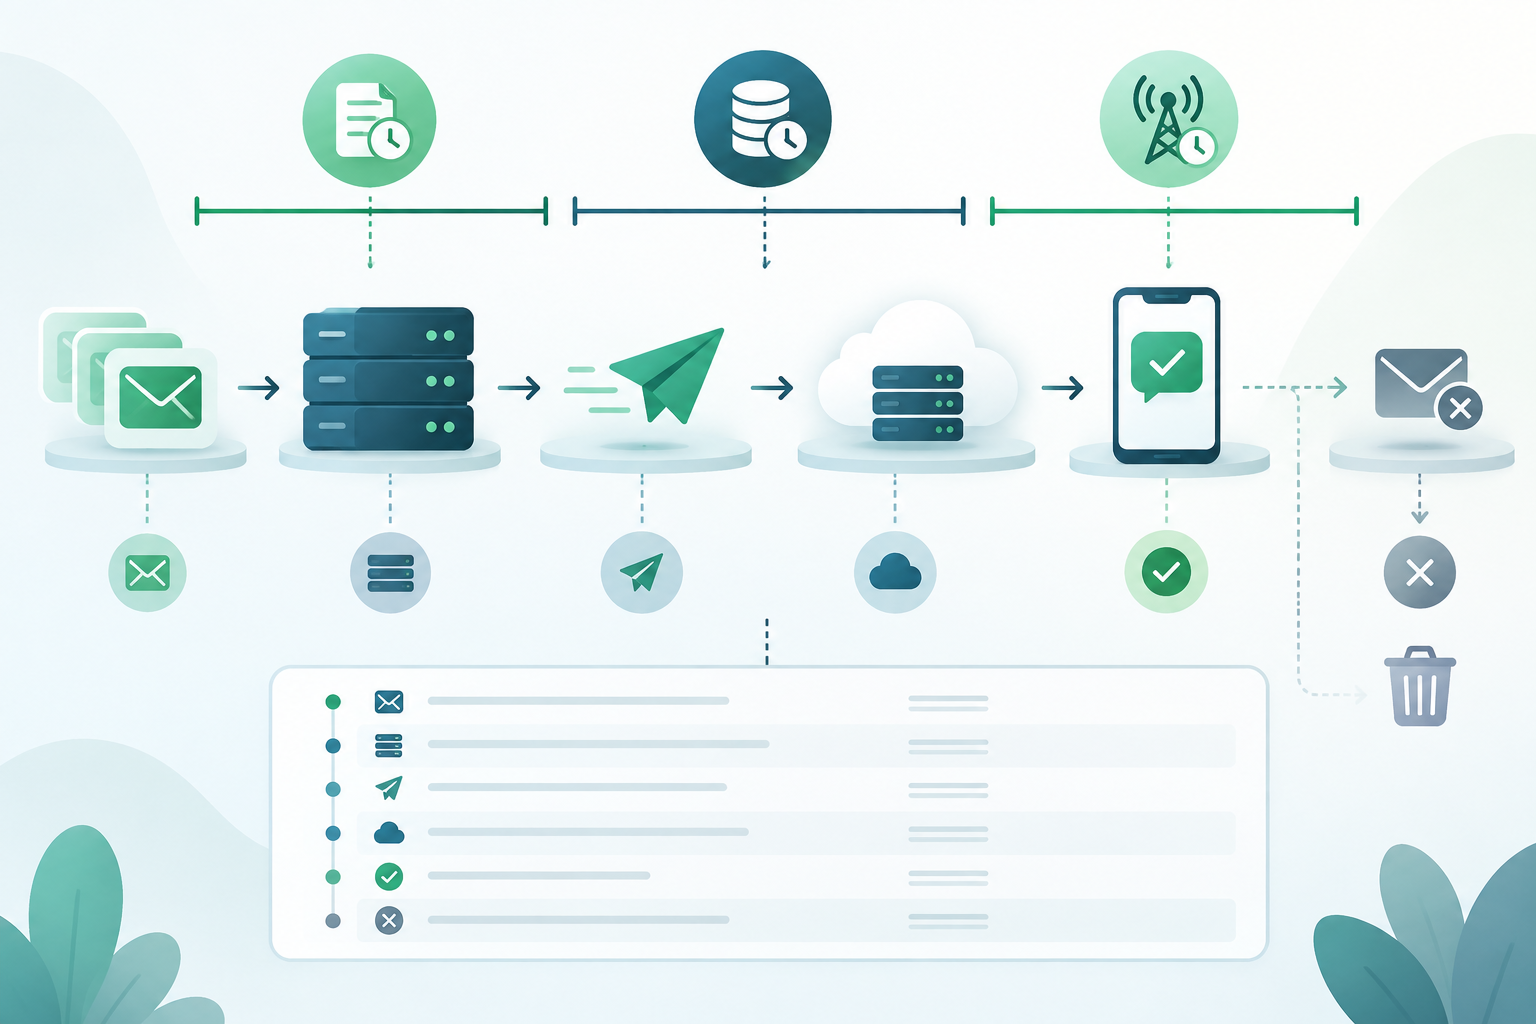
Three distinct limits: usefulness, internal queue, and provider expiry
A2P SMS expiration is not a single timer. Keep three controls separate: the functional deadline, which determines how long the message is useful to the recipient; the expiration policy for the internal queue or broker; and the validity period requested from the provider or service center.
The 3GPP-defined TP-Validity-Period specifies how long the service center retains the message before completing delivery. It is not the same as the application queue’s TTL. In addition, the implementation and scope of a platform’s expiry option vary by provider.
For example, Twilio documents a validity period for how long a message remains in its outbound queue. Its documentation also warns that after a message is sent to the carrier network, it could still be queued and delivered later. Do not treat this parameter as a guarantee that the message will be delivered before a deadline.
- Functional deadline: Until when would it still make sense for the recipient to receive this message?
- Internal TTL: How long does the broker allow it to remain available for processing?
- Provider validity: Which stage does the parameter documented for this connection cover?
- Confirm the meaning, limits, and behavior of each parameter in the applicable technical documentation.
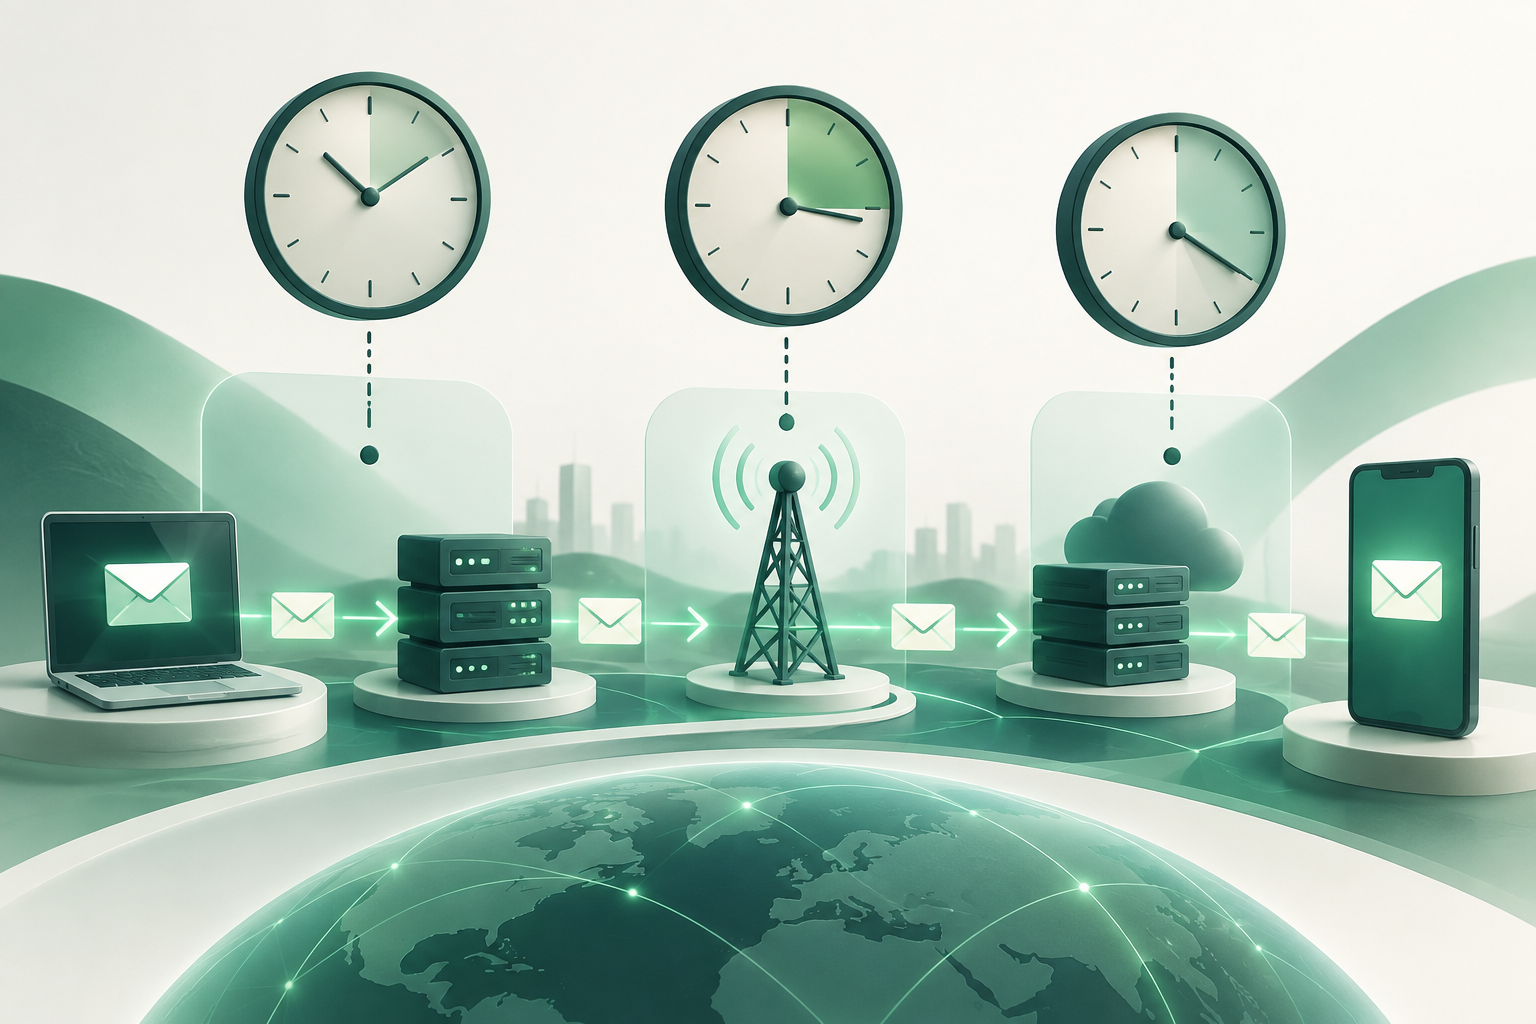
Why a recovered route can release stale messages
When a connection has limited capacity, some platforms queue requests to send later. If the route becomes available again, those messages may resume their journey. A backlog, by itself, does not make the content invalid or guarantee that the provider will discard it.
Before dispatching a held item, check its functional deadline. If it has expired, do not resend it simply because the connection has regained capacity. Broker expiration may help, but how it is enforced depends on the product and the message’s state. For example, Azure Service Bus documents specific behavior for expired messages and messages already under lock; these details should not be extrapolated to other brokers.
- Check functional validity just before sending, not only when the message is queued.
- When a route recovers, check for expiration before selecting eligible messages.
- Measure and alert on queue age; observed latency is not a substitute for an expiration rule.
- Verify how your broker handles expired messages, locked messages, and dead-letter items.
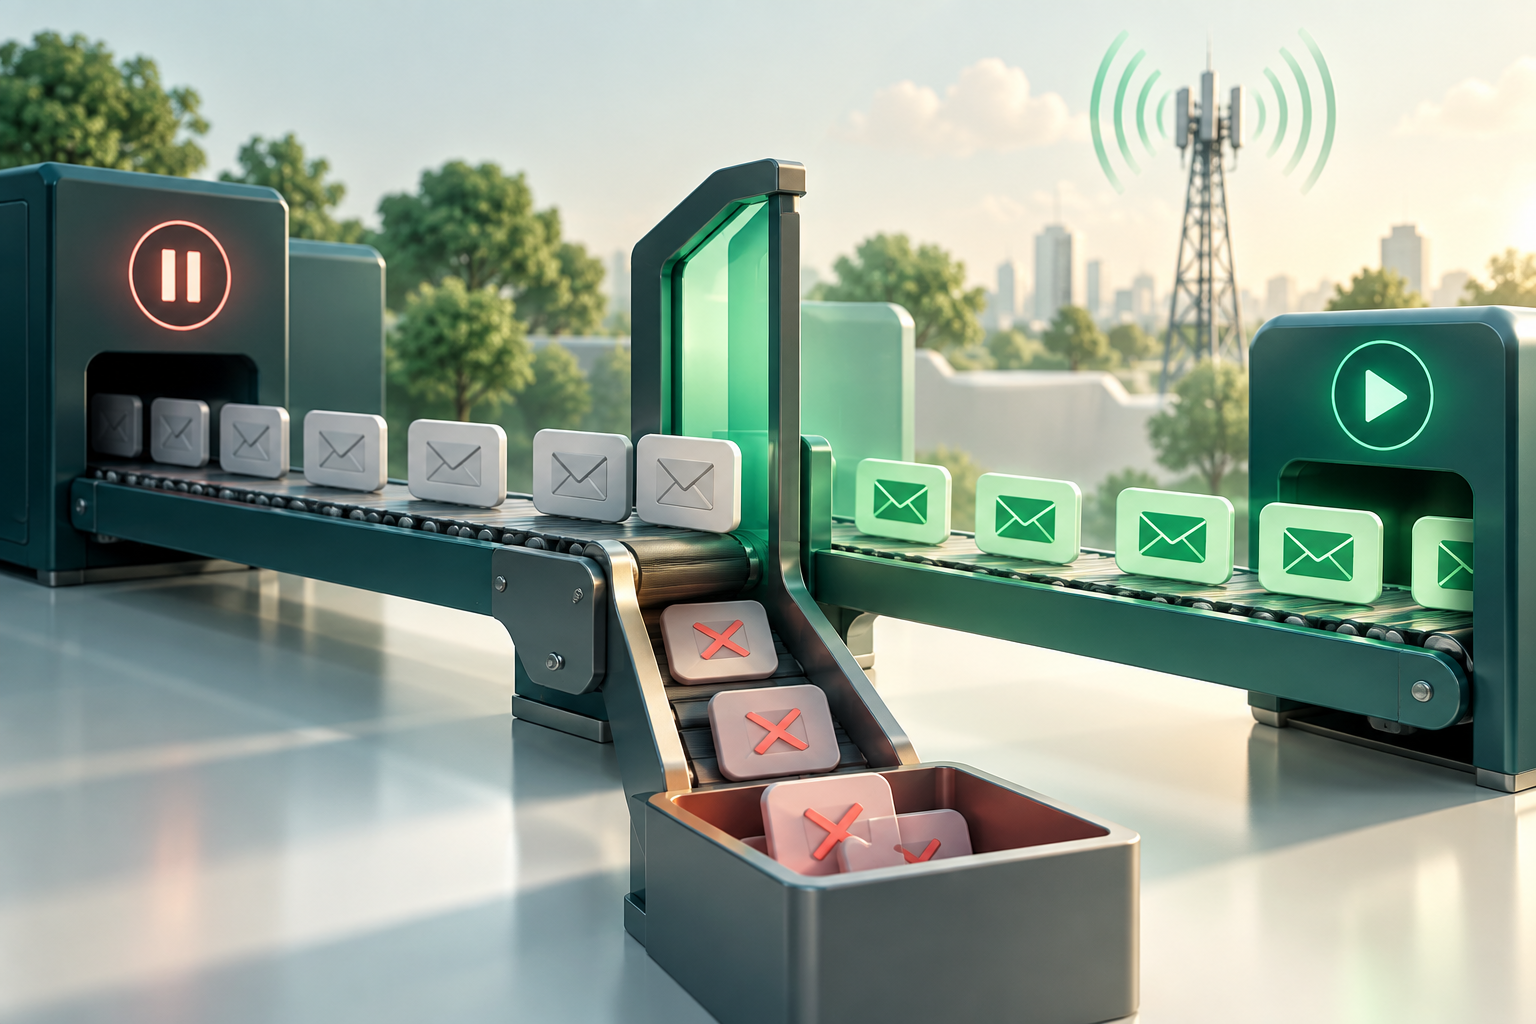
Define policies by traffic class
One duration does not work for every case. Derive the rule from the message’s time-sensitive usefulness and applicable requirements, then translate it into a verifiable deadline. Configure provider expiry and internal expiration separately when the architecture allows it.
For OTPs, NIST SP 800-63B-4 states that an out-of-band authentication must be considered invalid if it is not completed within 10 minutes, and that the secret must be accepted only once. OWASP also recommends a short TTL, single use, attempt limits, and invalidation after successful verification. This authentication limit is not a universal queue duration or a recommendation for other message classes.
Transactional alerts and non-urgent messages need their own rules. Set their expiration according to the operation they report, user expectations, and applicable obligations. If you cannot justify a specific duration, do not present it as a standard: document the rationale and validate the behavior.
- OTPs: The authentication system must reject expired codes and prevent reuse, even if the SMS arrives later.
- Transactional alerts: Define what makes them irrelevant and how to prevent a late notification from contradicting the current state.
- Non-urgent messages: Set a functional window appropriate to their purpose; do not automatically inherit the OTP configuration.
- For every category: Preserve applicable consent and compliance requirements, and do not resend promotional messages outside the relevant authorization.
Design the lifecycle and handle uncertain states carefully
Model the journey with explicit states: queued, eligible, sent to provider, accepted by carrier, expired, canceled, and closed with an uncertain outcome. Exact names vary; follow your platform’s contract and retain the mapping to its states.
Acceptance of a request does not mean the SMS has been delivered. In Twilio’s documentation, for example, “sent” indicates acceptance by the upstream carrier, while “delivered” depends on a later confirmation. A DLR or callback is a signal from the relevant system, not independent proof of human receipt or a universal guarantee of device confirmation.
If there is no conclusive outcome, keep the state as uncertain until a later event arrives or reconciliation is closed under a documented policy. Avoid automatic retries that could duplicate the message without assessing the risk.
- Store the functional deadline with the message identifier and check it at every processing transition.
- Distinguish request accepted, sent to the upstream carrier, and reported delivered; do not combine them into a single “success” state.
- Define which event closes an operation and how cases without a DLR or with contradictory states are reconciled.
- Protect OTPs: do not log their values in plain text as part of routine auditing.
Changing routes or purging: what to do with in-flight messages
An internal purge can prevent messages still under your system’s control from being processed, but you should not assume it can withdraw an SMS that has already entered the network. Cancellation options depend on the provider and the message’s state. For example, Twilio’s documentation describes canceling certain scheduled messages before their send time; this does not establish general cancellation after dispatch to the carrier.
When changing routes, separate items still in your queue from those already accepted by the provider. For the former, check the deadline and decide whether to hold, discard, or reroute them according to documented rules. For the latter, check statuses and receipts, but communicate the limits of your control: the message may continue its journey even after your local queue has been purged.
For a broad purge, define its scope by identifier, traffic class, route, time interval, or another verifiable operational criterion. Use a preview mode if available, and avoid indiscriminately deleting items whose state is uncertain.
- Pause or limit dispatch before changing rules, if the operational design allows it.
- Classify messages as still internal, handed to the provider, or of uncertain outcome.
- Cancel remotely only when the provider documents that action for the specific state.
- Do not claim that a purge will prevent delivery of messages already accepted by the network.
Make purges auditable and reconcilable
An operational purge should be reconstructable: what was removed, why, within what scope, and who authorized the action. Store timestamps and the identifiers needed to relate the local decision to provider statuses and later receipts.
An audit does not need to store the SMS body to be useful. In particular, avoid logging OTPs in plain text. If the broker supports dead-lettering for expired messages, it can help with review and reconciliation, but this capability must be explicitly enabled and configured; behavior depends on the broker.
- Record the reason, purge scope, authorized person or process, and timestamps.
- Retain correlation identifiers and before-and-after states, with restricted access.
- Do not routinely include sensitive content or authentication secrets in logs.
- Document retention, purge permissions, and the reconciliation procedure for expired or uncertain messages.
Test every connection and stage before relying on expiration
A parameter with the same name may have a different scope across providers. Check the documentation for the specific connection and run controlled tests in an appropriate environment with authorized recipients. Do not turn a one-off result into a guarantee for other operators, routes, or network states.
Observe internal queue expiration, the provider expiry request, acceptance statuses, and delivery receipts separately. Record what happens to queued, sent, and uncertain messages. Repeat tests after material configuration or connection changes, while respecting the provider’s limits and conditions.
- Confirm the units, permitted range, default value, and stage covered by each parameter.
- Test messages that expire before dispatch and messages whose state changes during the test.
- Compare local status with callbacks or receipts, and document cases without conclusive confirmation.
- Review broker and provider caveats; do not generalize results from one platform.
Operational checklist
Before enabling or changing a policy, make sure the team can identify expired messages, distinguish them from those already in flight, and explain what evidence it receives at each stage. The review should also cover permissions, alerts, and communication among operations, engineering, and product.
Each traffic class has a documented functional expiration criterion.
The consumer checks the deadline before dispatch, including after a route recovers.
Broker TTL and provider expiry are documented as separate controls.
Acceptance, sending, reported delivery, and uncertainty are not conflated.
- The purge has a defined scope, reason, authorization, timestamps, and reconciliation identifiers.
- There are alerts for queue age, buildup, expirations, and missing confirmation, with thresholds set by the team.
- Operational changes are communicated to affected teams and have a rollback procedure.
Frequently asked questions
Does requesting expiry from the provider guarantee that the SMS will not arrive late?
No. The scope depends on the provider. It may only limit how long the message stays in the provider’s platform queue; after acceptance, the mobile network could still queue and deliver it later.
Is my internal queue TTL equivalent to the 3GPP validity period?
No. Internal TTL governs your application or broker queue. The 3GPP TP-Validity-Period concerns how long the service center retains the SMS before completing delivery.
Can I cancel a message after the carrier has accepted it?
Do not assume so. Cancellation depends on the platform and the message’s state; check the provider’s documentation. A local purge does not prove that a message already handed to the network has been withdrawn.
What expiration should I use for OTPs?
NIST SP 800-63B-4 states that an out-of-band authentication must be considered invalid if it is not completed within 10 minutes, and that the secret must be used only once. Your queue rule and the provider’s rule are separate controls; also apply the relevant security and compliance requirements.
Does a “sent” status or a DLR prove that the recipient read the SMS?
No. Statuses depend on the platform and the receipts available. “Sent” may indicate acceptance by the upstream carrier, while a delivery status is a later technical confirmation; neither, on its own, proves that a person read the message.
Sources consulted
- 3GPP TS 23.040 Release 18, vía ETSIETSI / 3GPP
- Messages resource APITwilio
- Messaging Services: validity periodTwilio
- Outbound Message Status in Status CallbacksTwilio
- Error 30036: Validity Period ExpiredTwilio
- Message expiration and TTL in Azure Service BusMicrosoft Learn
- Enable dead lettering on message expirationMicrosoft Learn
- NIST SP 800-63B-4, sección sobre autenticadores fuera de bandaNIST
- Multifactor Authentication Cheat SheetOWASP