A2P SMS Traffic Admission Controls: How to Validate Each Flow Before Routing
An operational guide to documenting purpose, sender, destination, and message profile; applying pre-send checks; and handling exceptions without confusing eligibility with route quality.
Why Validate Admission Before Choosing a Route
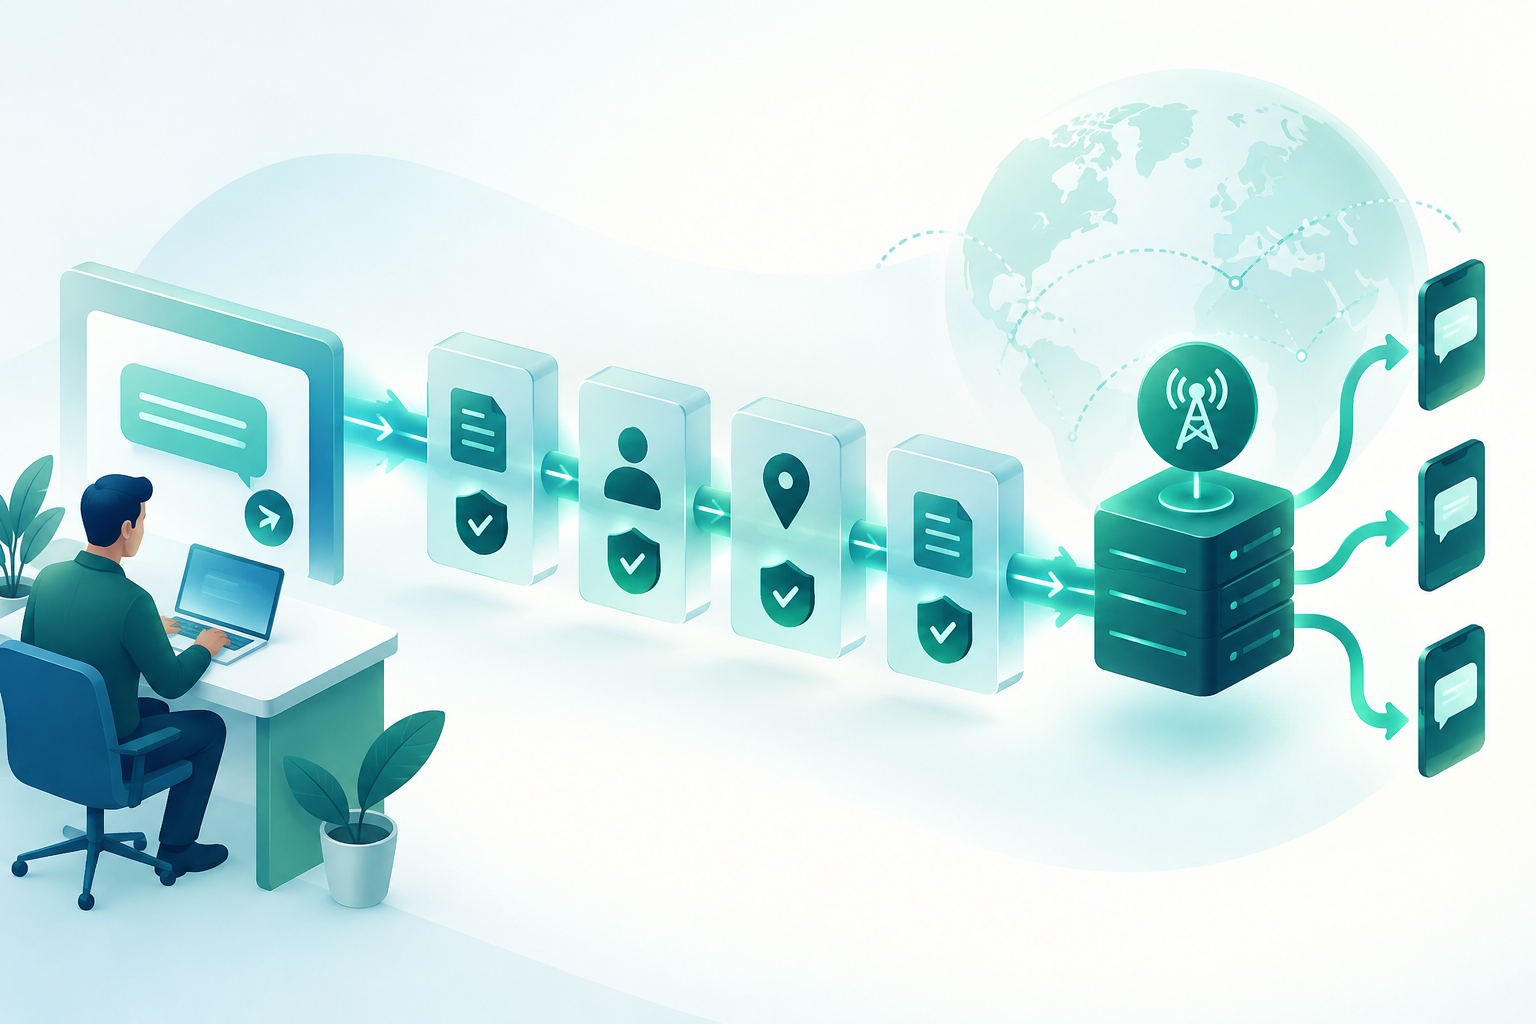
Route selection and flow admission are separate decisions. The first compares connectivity options for a destination; the second determines whether the traffic presented matches the documented conditions for that service. Validate eligibility first, then assess which available routes are appropriate.
These checks help prevent changes to a sender, purpose, or content from going unnoticed. They do not certify that a message will be delivered and do not replace the legal, contractual, or operator policy obligations that apply to the destination.
- Define the unit being checked: a customer, application, sender, campaign, or flow identified consistently.
- Separate the admission outcome—accept, reject, or send for review—from route quality metrics.
- Record the agreed conditions and who has authority to change them.
Which Conditions Should Be Explicit
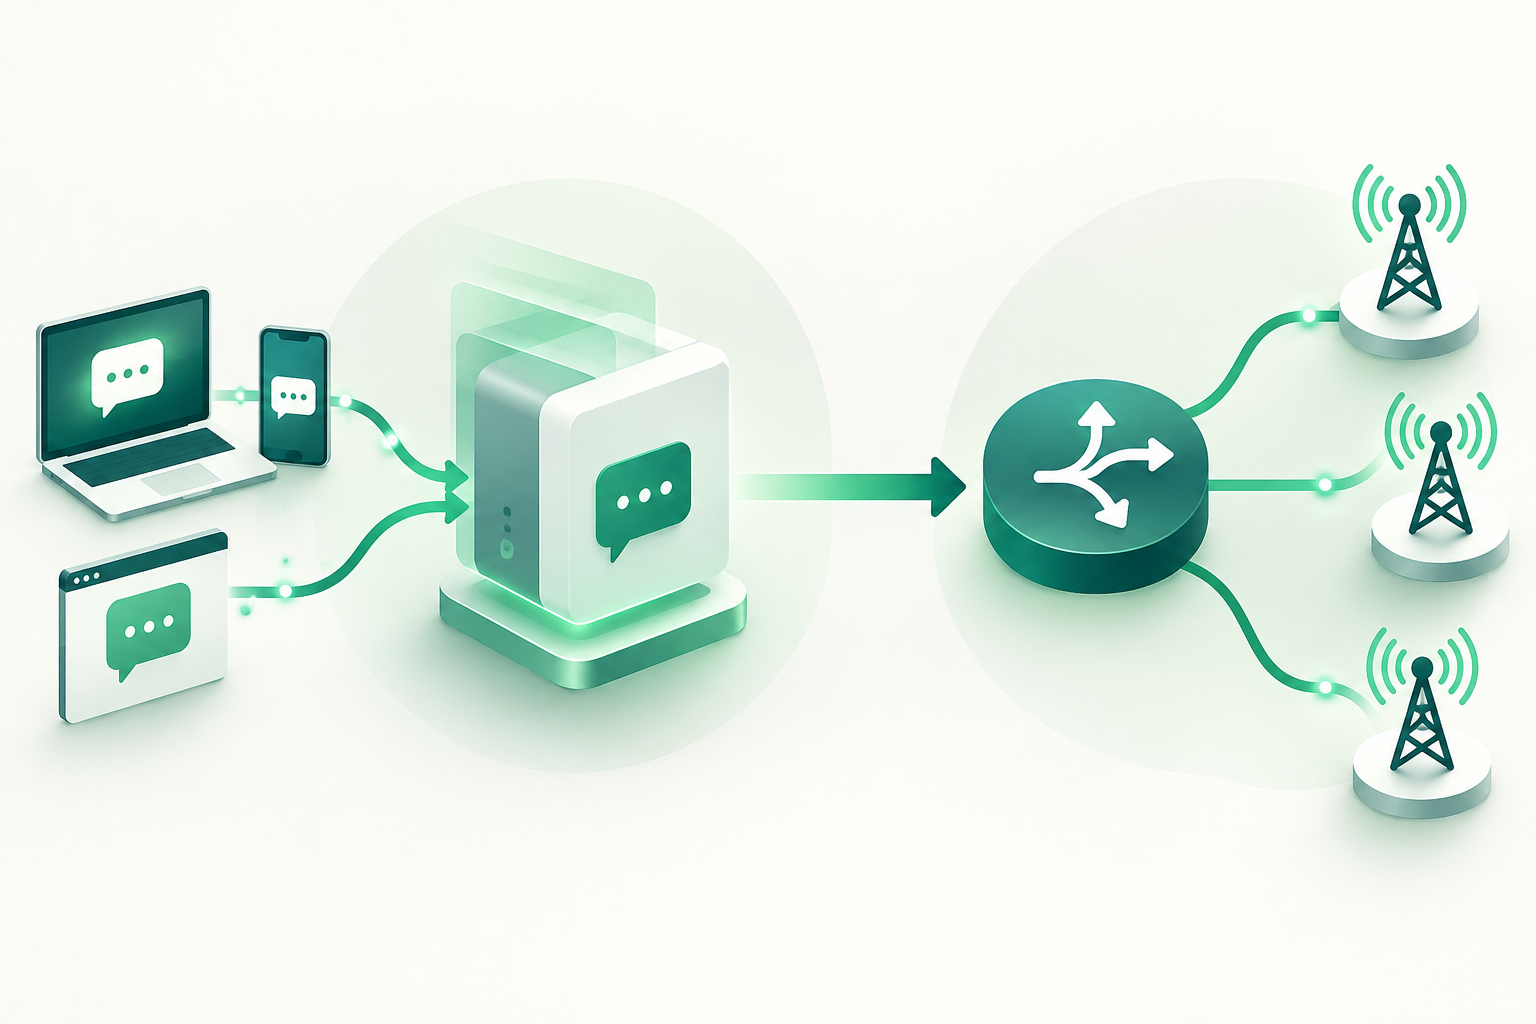
Before automating checks, translate the operational agreement into specific fields. At a minimum, document the declared purpose, permitted sender, included destinations, and expected content profile. Add conditions that are genuinely part of the agreement or applicable rules; do not assume a generic list covers every country and operator.
The content profile can describe the message type—for example, OTP, transactional, or marketing—its expected structure, variable types, and whether it contains links. If URLs are used, document which ones are permitted and how links must be declared, including shortened links where relevant. This is a useful operational criterion, but should not be presented as a universal requirement: Colombia’s CRC described requirements concerning templates and links within specific regulatory proposals.
- Purpose: the declared use and any uses outside the agreed scope.
- Sender: the permitted value or set of values, expected format, and authorization status when that information is available.
- Destination: the countries, networks, or other explicitly included areas, together with known restrictions.
- Content: message type, structure, expected variables, and the presence of URLs or other elements subject to conditions.
- Validity: the version of the conditions, review date, and person responsible for approval.
How to Turn Documented Conditions into Testable Rules
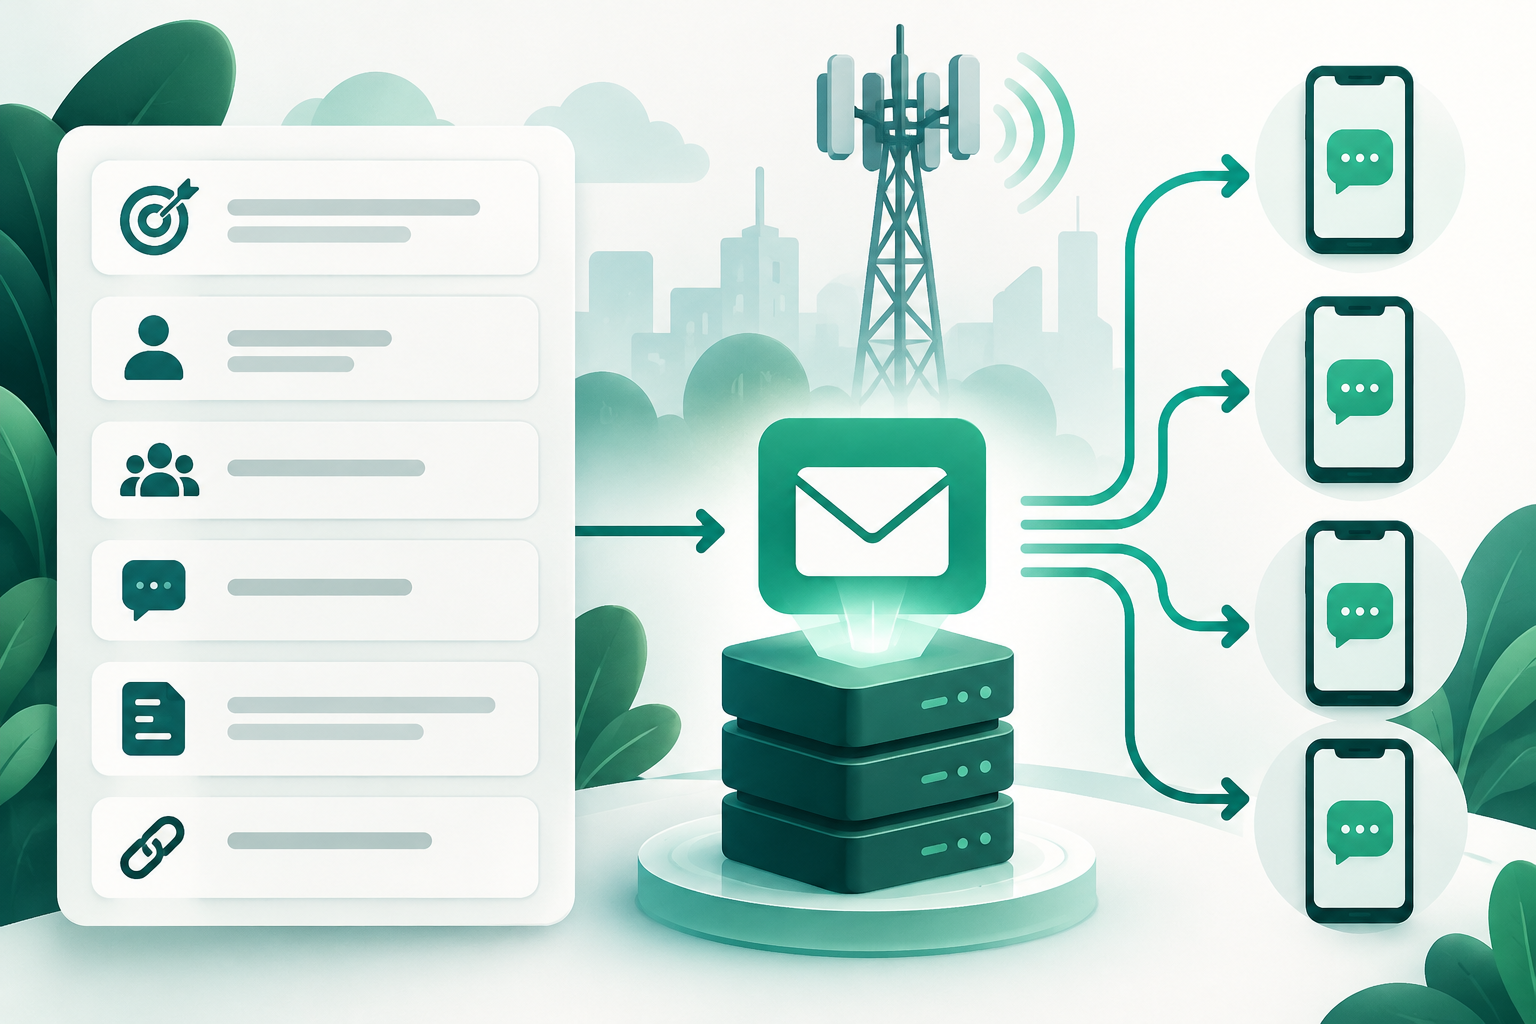
Each condition should become an observable test with a defined outcome. For example, if the sender must be on an authorized list, compare the incoming value with that list; if the destination is not covered by the agreement, stop the send or refer it for review rather than inferring authorization.
Do not turn an ambiguous description into a permissive rule. If the agreement only says “service messages” but does not define purposes or senders, ask for clarification before expanding admission. Rules can run in your own system or at the available integration point; do not assume an external platform implements these checks automatically.
- Write each rule as a condition, data source, and outcome for a match or mismatch.
- Use version-controlled lists or catalogs for senders, destinations, and profiles when required by the agreement.
- Define which fields are mandatory and what happens if they are missing.
- Test permitted, prohibited, and ambiguous cases before activating the control.
Checks When Onboarding a Customer, Sender, or Flow
When setting up a flow, request a record consistent with the commercial agreement and the destination’s rules. Check that the described purpose aligns with the content profile and that each sender and destination falls within the recorded scope. For later changes, compare the new configuration with the approved version; do not treat a material change as a routine technical update.
For templates, a CRC regulatory proposal in Colombia describes associating A2P messages with approved, current templates and respecting their declared structure, purpose, and message type, including when variable fields are used. That document does not by itself establish an obligation that applies to all countries or routes. It also clarifies that the described validation concerns static content and the meaning of dynamic fields, not necessarily each individual final message or the specific value of data such as an OTP.
- Confirm that the use description and requested profile are consistent.
- Verify sender authorization using the documented mechanism for that destination; do not assume there is a universal registry.
- Check that the destination is covered by the agreement and that known restrictions are reflected.
- Keep the approved profile version, date, and identity or role of the person who authorized onboarding.
What to Do with Missing, Incompatible, or Ambiguous Data
Missing data does not mean authorization. Establish a policy for each field: reject, hold, or request clarification. For attributes that determine eligibility—for example, purpose, sender, or destination—review is safer than filling in the gap with an assumption.
If two sources disagree, define which one is the current operational reference and who can resolve the conflict. Keep traffic under review until a discrepancy affecting the agreed scope is resolved. Do not “fix” traffic by changing senders, content, or routes to bypass filters or restrictions.
- Mandatory field missing: do not route until it is provided or the approved review procedure is applied.
- Data conflicts with the agreement: reject or suspend that flow and communicate the specific reason.
- Conflicting information: record the sources and escalate to the responsible person.
- Uncertainty about destination rules: confirm the requirement with the appropriate party before expanding scope.
Exception Management: Owner, Scope, and Evidence
An exception should be explicit, limited in scope, and reviewable. Record who requested it, who approved it, which customer and flow it covers, which condition it changes, and how long it is valid. If it has no defined expiry, set a review date and prevent a temporary exception from silently becoming the general rule.
Evidence should make it possible to reconstruct the decision without retaining unnecessary message content. Keep a reference to the agreement, the configuration version, and the rationale; limit access according to applicable privacy and security policies. Specific retention requirements depend on the legal and contractual context.
- Where the process allows, assign approval to someone other than the person or system performing the automated action.
- Limit the exception to the affected sender, destination, purpose, and profile.
- Set an expiry, review date, and conditions for revocation.
- Record the minimum necessary evidence and who can access it.
How to Review Changes Without Disrupting Legitimate Use
Not every change is a violation, but any change that alters accepted conditions deserves a proportionate assessment. Compare the new version with the previous one and determine whether the purpose, sender, destination, content structure, or use of links has changed. If the change is not covered, request clarification and approval before expanding admission.
To reduce disruption, communicate in advance what information is required and which flows are affected. If operational policy allows, leave already approved flows unchanged and isolate only the new sender or pending profile. Do not promise continuity when destination or operator rules require a different response.
- Compare versions and classify the change as technical, editorial, or material to eligibility.
- Request a new review when the purpose, sender, destinations, or agreed profile changes.
- Define how existing traffic will be handled during the review, in line with the contract and applicable rules.
- Document the decision and update rules only after approval.
Recording Decisions for Operational Audits
A useful record should explain what was assessed, which version of the conditions was used, and what the outcome was. Keep admission and rejection events separate from quality metrics: correct admission does not prove delivery, and reported delivery does not prove that traffic was authorized.
If DLRs are used, distinguish the status reported by the messaging chain from verified receipt on the device. Admission and delivery, latency, or availability metrics answer different questions and may each have their own uncertainty.
- Include the flow identifier, date and time, destination, rules version, and outcome.
- Record a normalized reason for rejection or review, and the action taken.
- Link exceptions and approvals using a reference, without duplicating sensitive data.
- Periodically review repeated rejections, frequent changes, and rules that create ambiguity.
Frequently asked questions
Are these controls universal requirements for all A2P routes?
No. They are an operational practice for translating agreements and applicable rules into checks. Requirements depend on the country, operator, contract, and type of traffic. The cited CRC references describe specific proposals in Colombia and do not, by themselves, establish a universal or current rule for every route.
Does validating a sender prove that consent was obtained?
No. A sender’s authorization or inclusion in a registry does not, by itself, prove recipient consent, the sender’s identity, or the legality of every message. Those matters require controls and evidence appropriate to the case and jurisdiction.
Does accepting a flow guarantee that the SMS will reach the phone?
No. Acceptance means that the traffic passed the defined admission checks. It does not guarantee routing, delivery to the device, or that a DLR amounts to verified receipt.
Should every dynamic OTP value be reviewed before sending?
A universal requirement cannot be inferred from the available documentation. The CRC response concerning the proposal described distinguishes validation of the structure and meaning of dynamic fields from review of the specific OTP value. Apply the requirements of the agreement, applicable rules, and privacy design.
What should happen if the purpose or destination is missing?
Define a fail-safe policy in advance: stop, hold for review, or request the missing data. Do not infer authorization from incomplete information or choose a route to avoid a restriction.
Sources consulted
- Documento de soporte: Identificación de medidas para mitigar el fraude cibernético por medio de servicios móvilesComisión de Regulación de Comunicaciones (CRC), Colombia
- Documento de respuesta a comentarios sobre medidas contra fraude en servicios móvilesComisión de Regulación de Comunicaciones (CRC), Colombia